Decide who needs the document and what they need to do
Before changing any settings, identify the people who need the document and the task each person must complete. A colleague checking figures may need to view a file, while the person correcting them needs edit access. Someone who only needs the final result may be better served by a separate, finalized copy. Starting with the task makes it easier to avoid granting broad access out of convenience.
Use the narrowest permission that allows the work to happen. Common choices include owner, editor, commenter, and viewer, although names and capabilities vary by platform. Check what each role actually permits: an editor may be able to change content, invite others, or remove material. If your service offers separate controls for downloading, printing, copying, or resharing, consider those too. Such restrictions can reduce casual spread, but they cannot prevent someone from photographing a screen or repeating information they have seen.
Share with named people, not an open link
For a confidential file, a named-person invitation is usually easier to control than a link that works for anyone who has it. Enter the intended recipients directly and confirm their email addresses before sending. Similar names, autocomplete suggestions, and personal versus work accounts can lead to accidental invitations. If a recipient does not have an approved account, pause and agree on a suitable way to share rather than loosening the link setting without checking.
Link settings deserve a separate review. “Anyone with the link,” “people in the organization,” and “specific people” can have very different reach. An organization-wide link may be convenient for a general reference sheet but too broad for a confidential client document. If a link must be used, choose the most limited audience and role available, and set an expiration when the service supports it. Test the recipient’s experience if practical, without using a public or unrestricted link as a shortcut.
Keep folders and copies under control
A document’s location can determine who gets access. A file placed inside a shared folder may inherit permissions from that folder, so inspect folder membership before adding confidential material. Avoid keeping sensitive drafts in a general team folder simply because it is the easiest place to find. A dedicated project folder with a small, clearly named group can make access easier to understand and maintain.
Permissions on the original file may not follow copies. Email attachments, downloaded files, exported PDFs, and documents moved to another service can each become separate items to manage. When several people need to work on the same content, sharing one controlled file may be simpler than sending multiple attachments. Before circulating a copy, check whether it contains comments, tracked changes, hidden sheets, or earlier content that the recipient does not need.
Give outside collaborators limited, time-bound access
External partners often need access for only one stage of a project. Share the specific file or project folder they need rather than a broader internal workspace. Give view or comment access unless editing is necessary, and confirm whether the platform lets guests invite other people. Where available, an expiration date provides a useful reminder, but it does not replace a manual check when the work is finished.
Account safeguards matter alongside document settings. Encourage collaborators to use their own accounts rather than a shared login, so access can be removed for one person without disrupting everyone else. If your workspace supports multi-factor authentication and activity records, use them according to your organization’s practices. These features can help protect accounts and clarify what happened, but they do not correct an overly broad invitation.
Review access as part of the document workflow
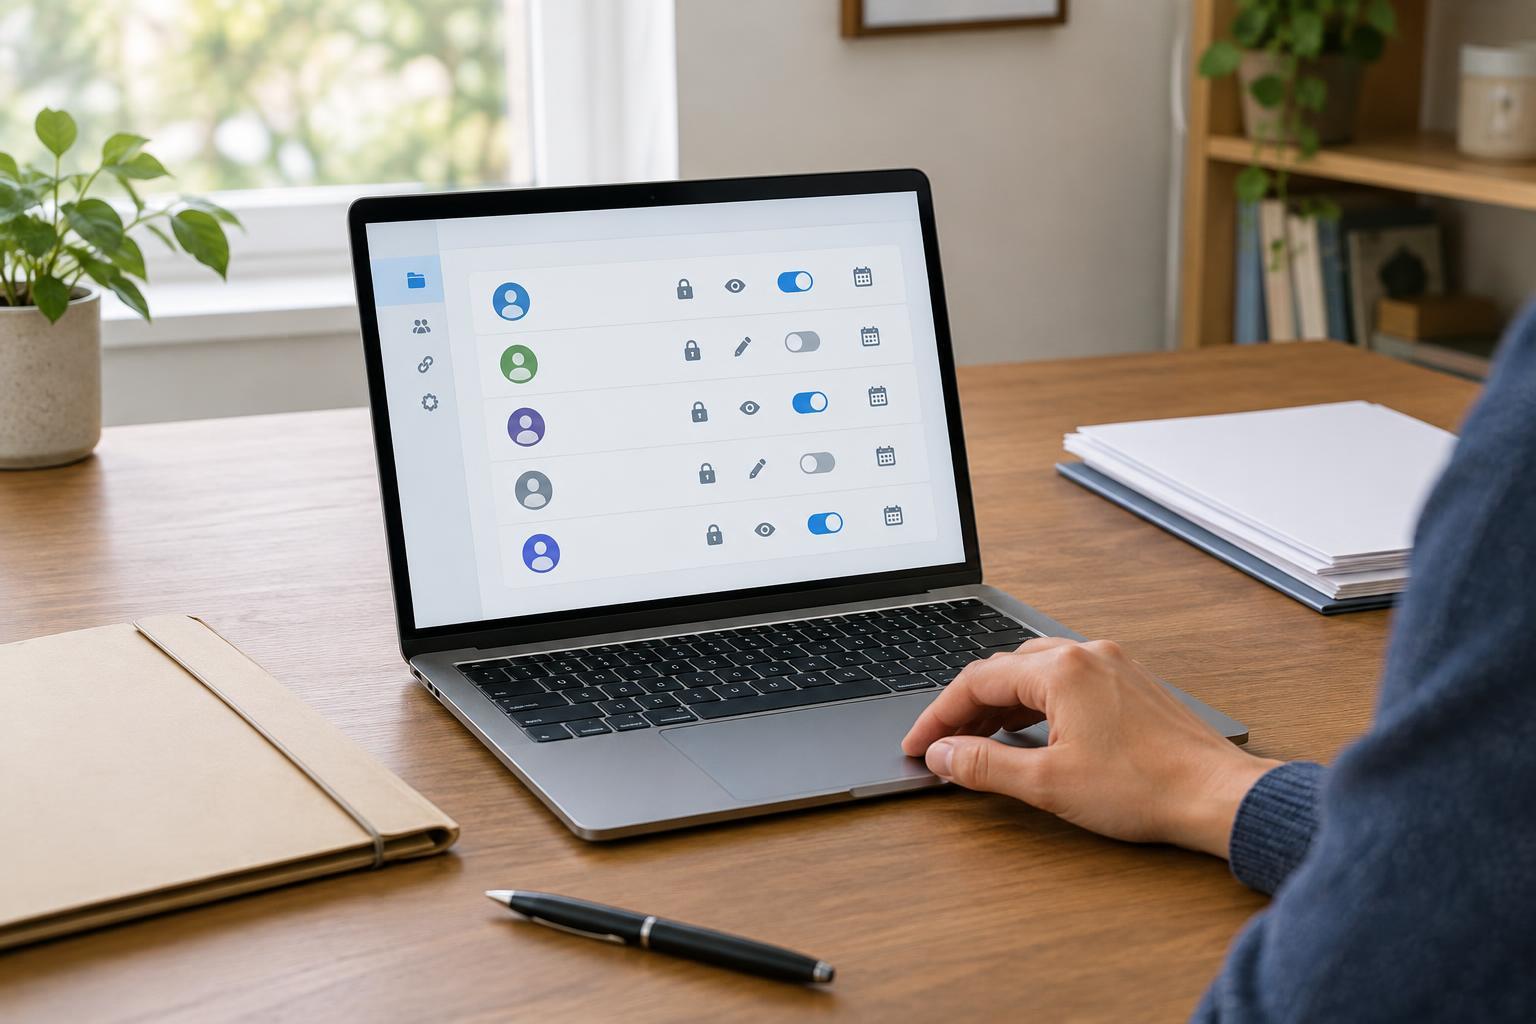
Set a point at which someone checks permissions: before sharing a draft, when a new person joins, and when a project closes. In the file’s sharing panel, review both direct invitations and access inherited from folders or groups. Remove people who no longer need the document, turn off links that have served their purpose, and verify who owns the file so it does not become difficult to manage when a staff member leaves.
For recurring work, a short checklist can prevent rushed decisions: confirm the file and folder, choose named recipients, assign the least necessary role, inspect link settings, and note when access should end. If confidential information was shared with the wrong person, stop further access promptly and follow your organization’s reporting process. Permissions work best as an ongoing habit, not a setting applied once and forgotten.